Breaking News & Latest Updates from the Tech World
Google Bans Android TV Manufacturer After 1.3 Million Devices Are Infected With Malware Backdoor
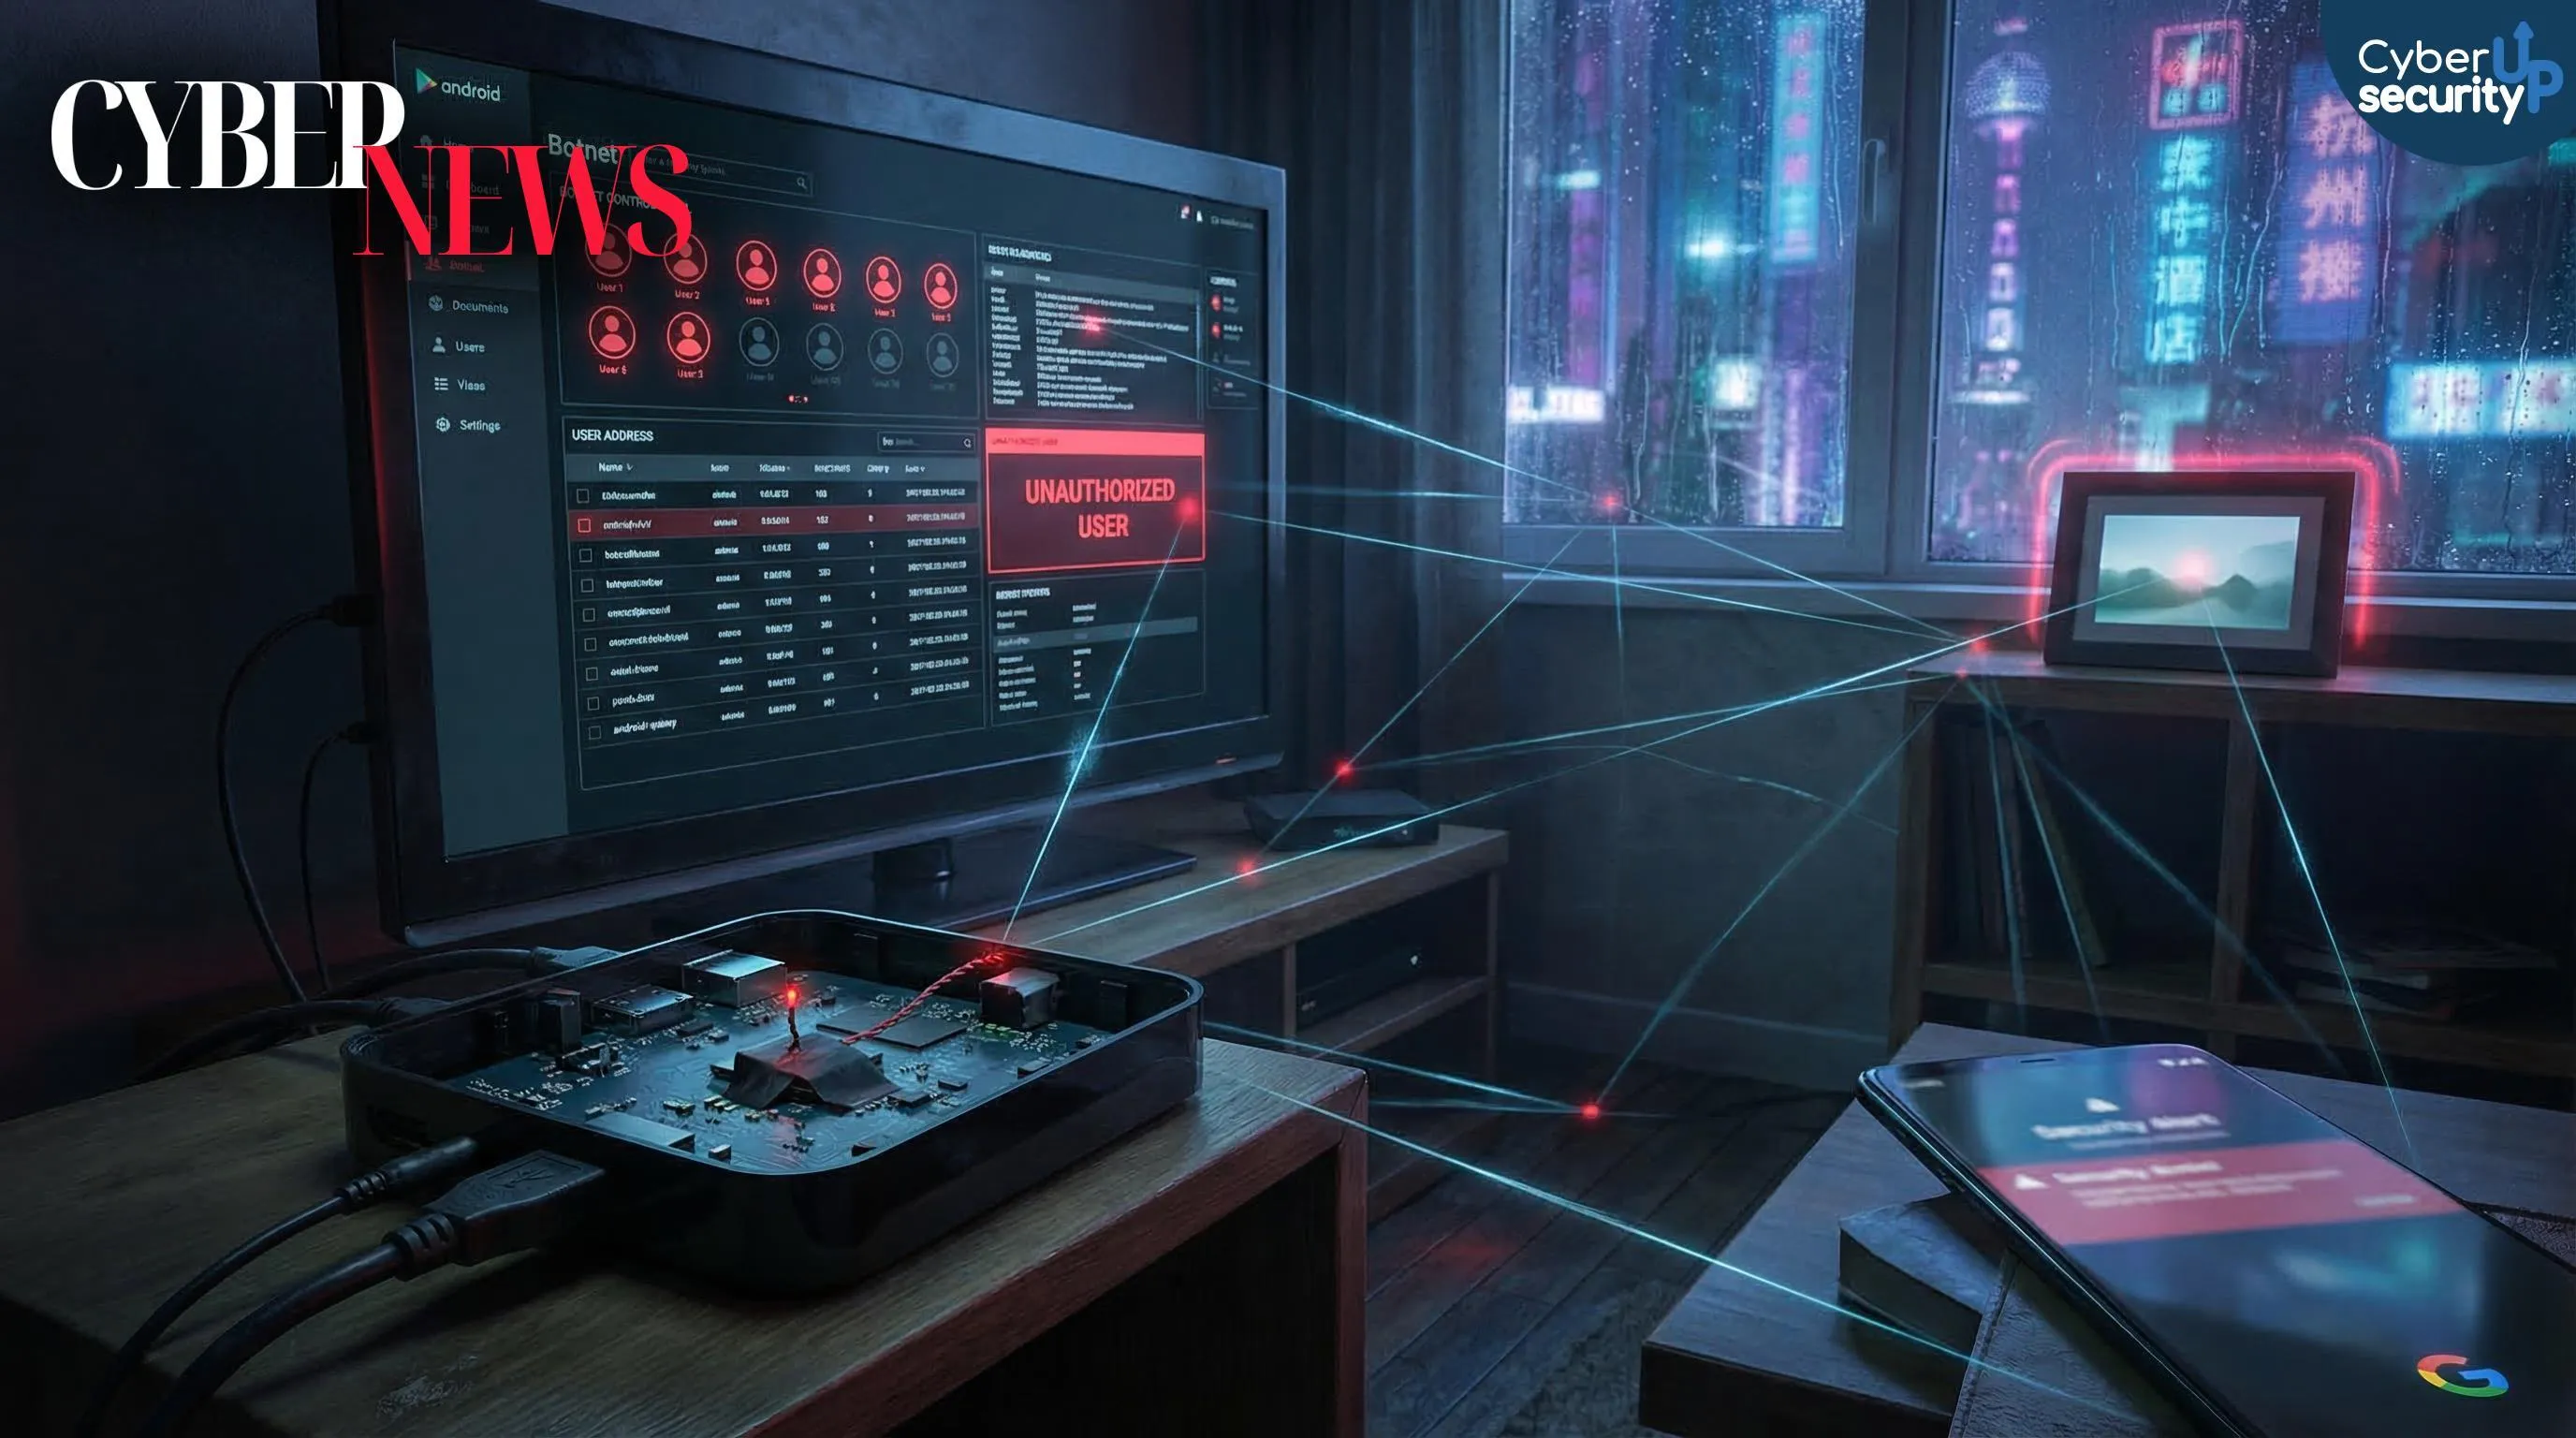
A massive cybersecurity investigation has uncovered a global botnet hidden inside Android TV boxes and other smart devices. Google has cut ties with the manufacturer Videostrong Technology after discovering that its devices were being used for cybercrime without users' knowledge.
1. Introduction: When Your Android TV Box Becomes a Cybercrime Tool
Android TV boxes have become increasingly popular because they offer an affordable way to turn ordinary televisions into smart entertainment systems. However, a recent cybersecurity investigation has revealed a disturbing security problem involving millions of these devices.
Google, working alongside cybersecurity researchers and Japanese law enforcement, has dismantled a massive botnet operation known as X.CPE.
The investigation identified more than 1.3 million infected devices distributed across over 200 countries. Most were Android TV set-top boxes, although other Android-powered devices, including karaoke machines, digital signage systems and telehealth equipment, were also affected.
The investigation linked the operation to Videostrong Technology, a Chinese original equipment manufacturer (OEM) that produced Android-based devices for different brands.
What makes this case particularly concerning is that the malicious software was reportedly built directly into device firmware before the products reached consumers.
This means users did not necessarily download a suspicious application, visit a malicious website or make a mistake. In many cases, the security compromise was already present when they purchased their devices.
2. What Actually Happened?
According to Google's Threat Intelligence Group, the X.CPE operation was not simply another malware infection spreading through suspicious downloads.
Instead, investigators discovered a backdoor integrated into the firmware of multiple device models over several years.
The malware operated with system-level privileges, giving its operators significant control over infected devices.
Google attributed the campaign to Videostrong Technology with high confidence and concluded that it was designed to generate revenue by providing access to infected devices to criminal affiliates.
The operation reportedly evolved over time, becoming more sophisticated and difficult to detect.
Rather than relying on one malicious application, the attackers developed a modular system that could install different malware components depending on their objectives.
This made the compromised devices useful for multiple forms of cybercrime.
3. How Did the X.CPE Malware Work?
One of the most concerning findings is how deeply the malware was integrated into the Android operating environment.
Google's investigation identified several important components.
A. Persistent System-Level Backdoor
The primary malware component, identified as x.cpe and in some versions as com.oemservice, was preloaded into the device firmware.
It operated with Android system-level privileges.
Even when users attempted to uninstall the malicious application, it could reinstall itself after a device reboot because another copy remained in the OEM partition.
This is significantly more dangerous than an ordinary unwanted application.
A typical application can often be removed through Android settings. However, malware embedded in system firmware can survive normal removal attempts.
B. Remote Command Execution
The backdoor communicated with external command-and-control (C2) infrastructure.
This allowed its operators to send instructions to infected devices, download additional components and execute remote commands.
Google's technical investigation also documented capabilities involving:
Remote shell command execution.
Downloading and executing scripts.
Installing additional malware.
Collecting device and system information.
Capturing screenshots.
Injecting keystrokes.
Monitoring network environments.
Disabling Google Play Protect verification.
These capabilities demonstrate that the threat extended well beyond ordinary advertising malware.
C. Modular Malware Installation
The X.CPE infrastructure could load additional malicious modules.
Researchers identified several malware families and components associated with the broader operation, including Spirit, Moyu, Bird and Fission.
These components could perform different tasks, including ad fraud, additional backdoor operations and residential proxy activities.
This modular architecture allowed the operators to change their monetization strategy without completely replacing the original infection mechanism.
4. How Were Infected Devices Used?
The most significant concern is that infected devices were reportedly monetized through multiple criminal activities.
Residential Proxy Networks
This was one of the primary monetization methods.
A residential proxy allows internet traffic to pass through a real household's internet connection and IP address.
In this case, infected Android TV boxes could be turned into proxy exit nodes without the owners knowing.
Cybercriminals could use these connections to route their traffic through ordinary residential networks.
This creates several potential problems:
Suspicious activity may appear to originate from an innocent household.
A household's public IP address may become associated with malicious traffic.
The owner's internet bandwidth can be consumed without permission.
The connection could be used to conceal the origin of other cybercriminal activities.
In other words, your internet connection could become part of a criminal network while you are simply watching television.
Advertising Fraud
The malware ecosystem also supported advertising fraud.
Some modules were designed to generate fraudulent advertising interactions or manipulate advertising-related activity in the background.
This creates financial losses for advertisers and advertising platforms.
Data Collection and Exfiltration
Google also reported observing operators collecting sensitive device information, account-related information, installed application inventories and system logs.
Some observed activities included capturing screenshots and executing commands remotely.
This raises serious privacy concerns, particularly when the device is connected to a household network.
Additional Malware Distribution
The compromised devices could also receive additional malicious applications and modules.
This means the original backdoor was not necessarily the final threat. It could serve as an entry point for other criminal operations.
5. Why Is This Case Different From Ordinary Android Malware?
Most users understand that downloading applications from unknown websites can be dangerous.
However, this incident highlights a different kind of security problem: supply-chain compromise.
In a traditional malware attack, the user may unknowingly install a malicious application.
In a supply-chain attack, the malicious component is introduced before the product reaches the customer.
That changes the entire security equation.
Even users who follow good security practices may unknowingly purchase compromised hardware.
The situation becomes even more concerning when the devices carry Google certification or branding, because consumers may reasonably assume that certification means the device has passed appropriate security checks.
Google acknowledged that Videostrong used obfuscation techniques to exploit gaps in its certification testing process.
The company has said it is improving its review process to prevent similar incidents.
6. Google's Response: Manufacturer Banned From Android Certification
Following the investigation, Google took several significant actions.
These included:
Taking legal action to disrupt the domains and servers used to control the X.CPE botnet.
Targeting command-and-control infrastructure associated with additional malware families.
Ending its relationship with Videostrong Technology.
Banning Videostrong and its future subsidiaries or affiliates from manufacturing and selling certified Android devices or supplying software to certified vendors.
Improving its Android device firmware integrity and security review processes.
Google also worked with Japan's National Police Agency and cybersecurity organizations, including TrendAI, HUMAN Security, Synthient and other industry partners.
However, one important distinction should be made: Google did not announce that it had legally shut down Videostrong as a company. It cut ties with the manufacturer and banned it from participating in its certified Android device ecosystem.
This is an important difference when interpreting the headline.
7. Is Your Android TV Box Still Dangerous?
This is perhaps the most important question for consumers.
Google says the disruption of the command-and-control infrastructure has effectively rendered the malware benign.
However, this does not necessarily mean that every infected device has been cleaned.
The original malware components may remain installed in the device firmware even after their communication infrastructure has been disrupted.
Some components may also be difficult to remove through normal factory resets or application uninstallation.
There is another concern: Google has not publicly confirmed a comprehensive forced cleanup process for every affected device.
Therefore, users should not assume that an infected device is permanently clean simply because the botnet infrastructure has been disrupted.
What Should Android TV Box Owners Do?
Here are some practical recommendations:
1. Check Your Device Manufacturer
Find the manufacturer and model number of your Android TV box.
Pay particular attention to inexpensive, unbranded or white-label Android TV boxes.
2. Check Whether Your Model Is Affected
Compare your device model against the security research published by the investigation partners.
Do not assume that every Android TV box is infected.
3. Avoid Untrusted Firmware
Do not install firmware from unknown websites or unofficial sources.
An unofficial firmware update could introduce additional security problems.
4. Review Security Settings
Check whether Google Play Protect is enabled where supported.
Also review installed applications and remove software that you do not recognize, although removing an application may not eliminate firmware-level malware.
5. Consider Disconnecting Suspicious Devices
If your device is identified as compromised and you cannot establish that it has been safely cleaned, disconnect it from your home network until you can obtain reliable manufacturer or security guidance.
6. Buy From Reputable Manufacturers
Choose devices from established manufacturers with transparent security updates and official support.
A low price should never be the only deciding factor when purchasing an internet-connected device.
8. Our Analysis: The Bigger Problem Is Hardware Trust
In our assessment, this incident is much more serious than a typical Android TV malware story.
The biggest problem is not simply that 1.3 million devices became part of a botnet.
It is that the reported infection mechanism existed at the hardware supply-chain level.
Consumers generally have limited visibility into what happens inside a device before it reaches their homes.
They cannot easily inspect firmware, verify every system component or determine whether a manufacturer has included hidden software.
This creates a significant trust problem.
Google's Certification Process Needs Stronger Protection
Google certification is intended to help ensure that devices meet compatibility and security requirements.
But this incident demonstrates that passing security checks at one stage does not necessarily guarantee firmware integrity throughout the device's lifecycle.
Manufacturers and platform providers need stronger controls, including:
Continuous firmware integrity verification.
Stronger checks after the first device boot.
Independent security audits.
Better monitoring of privileged system applications.
More transparent security update policies.
Stronger accountability for OEM partners.
Affordable Hardware Should Not Mean Reduced Security
Low-cost Android TV boxes are attractive because they provide smart features at affordable prices.
However, consumers often have little information about the companies manufacturing these products.
Some devices may use generic branding, limited software support and unclear update policies.
This creates an environment where security problems can remain unnoticed for long periods.
The responsibility should not fall entirely on consumers. Manufacturers, certification authorities, software platforms and online marketplaces all have important roles in protecting the hardware supply chain.
9. Final Verdict
The X.CPE botnet investigation exposes a serious weakness in the connected-device ecosystem.
It demonstrates that even an ordinary entertainment device can become part of a sophisticated cybercrime infrastructure when security is compromised at the manufacturing level.
Google's action against Videostrong is an important step, and disrupting the botnet's command-and-control infrastructure may significantly reduce the immediate threat.
However, disruption is not the same as complete remediation.
Consumers still need clear information about affected models, firmware cleanup options and long-term security support.
Our biggest takeaway is simple:
A smart device should not require users to become cybersecurity experts just to trust the product they have purchased.
Manufacturers must take responsibility for the software and firmware they ship. Platform providers must strengthen their certification processes, and consumers should prioritize security and long-term support over price alone.
The X.CPE incident is a reminder that cybersecurity starts long before a device is switched on for the first time.
Overall Assessment: A major supply-chain security failure that raises important questions about Android device certification, manufacturer accountability and consumer privacy.
Reviews & Comments (0)
No comments yet. Be the first to share your thoughts!
shahinur alalm
Expert reviewer and tech enthusiast at SamReview.